What it looks for
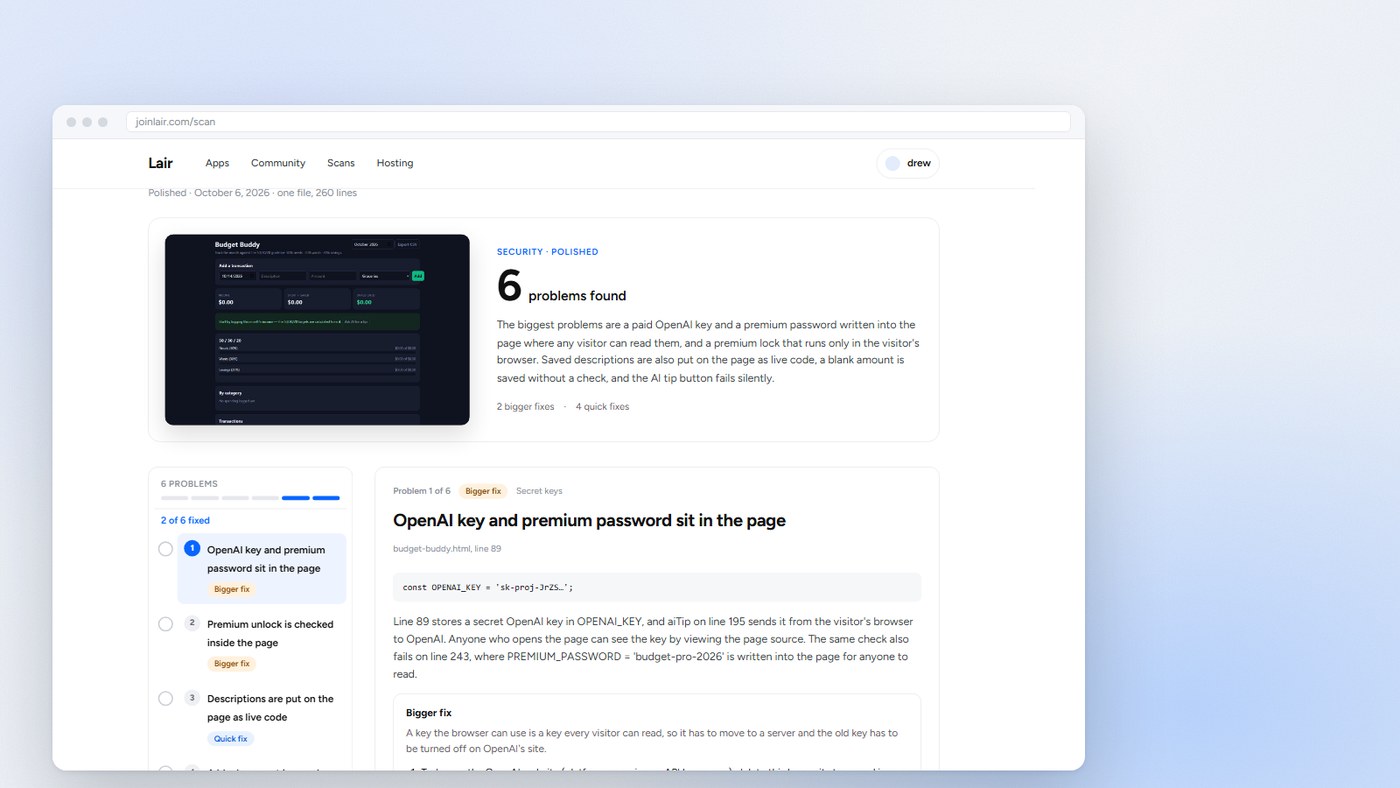
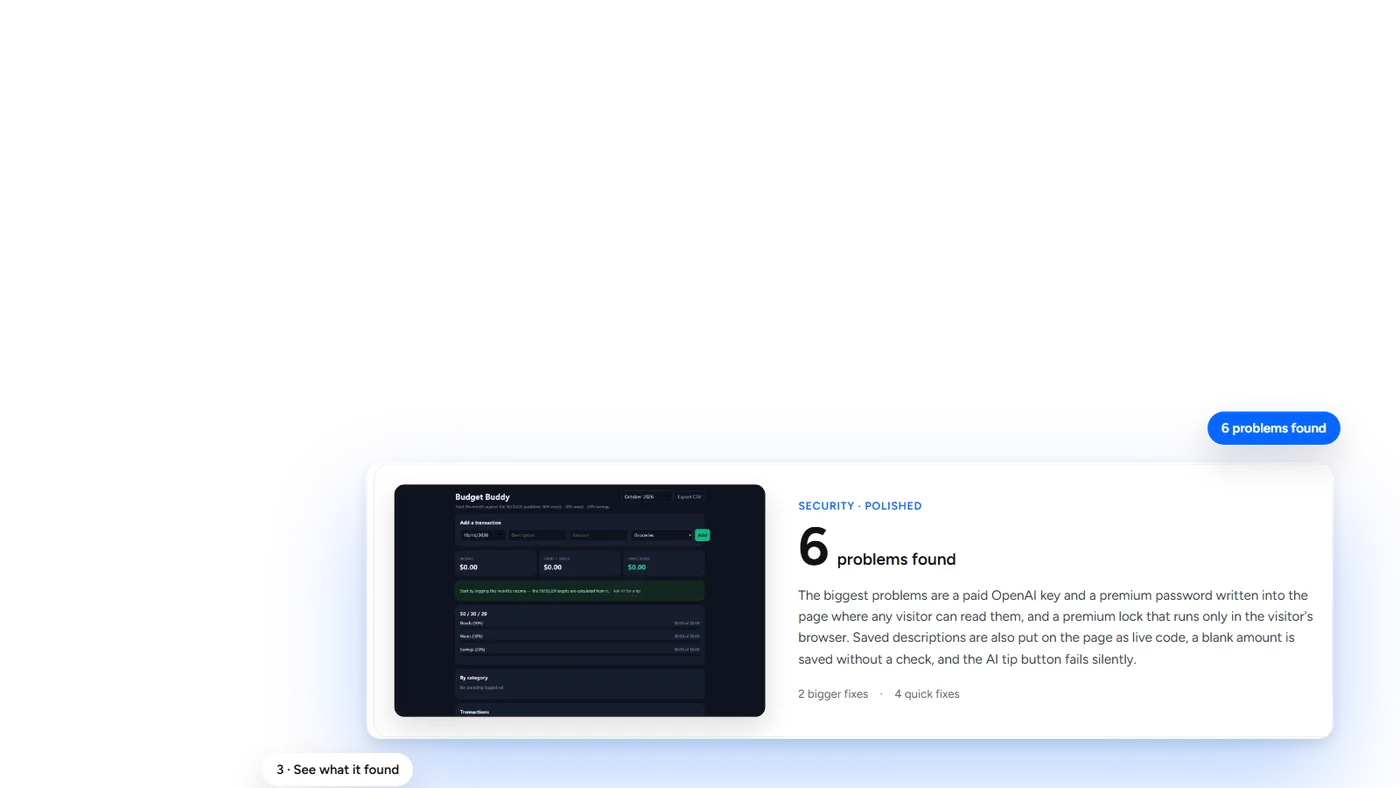
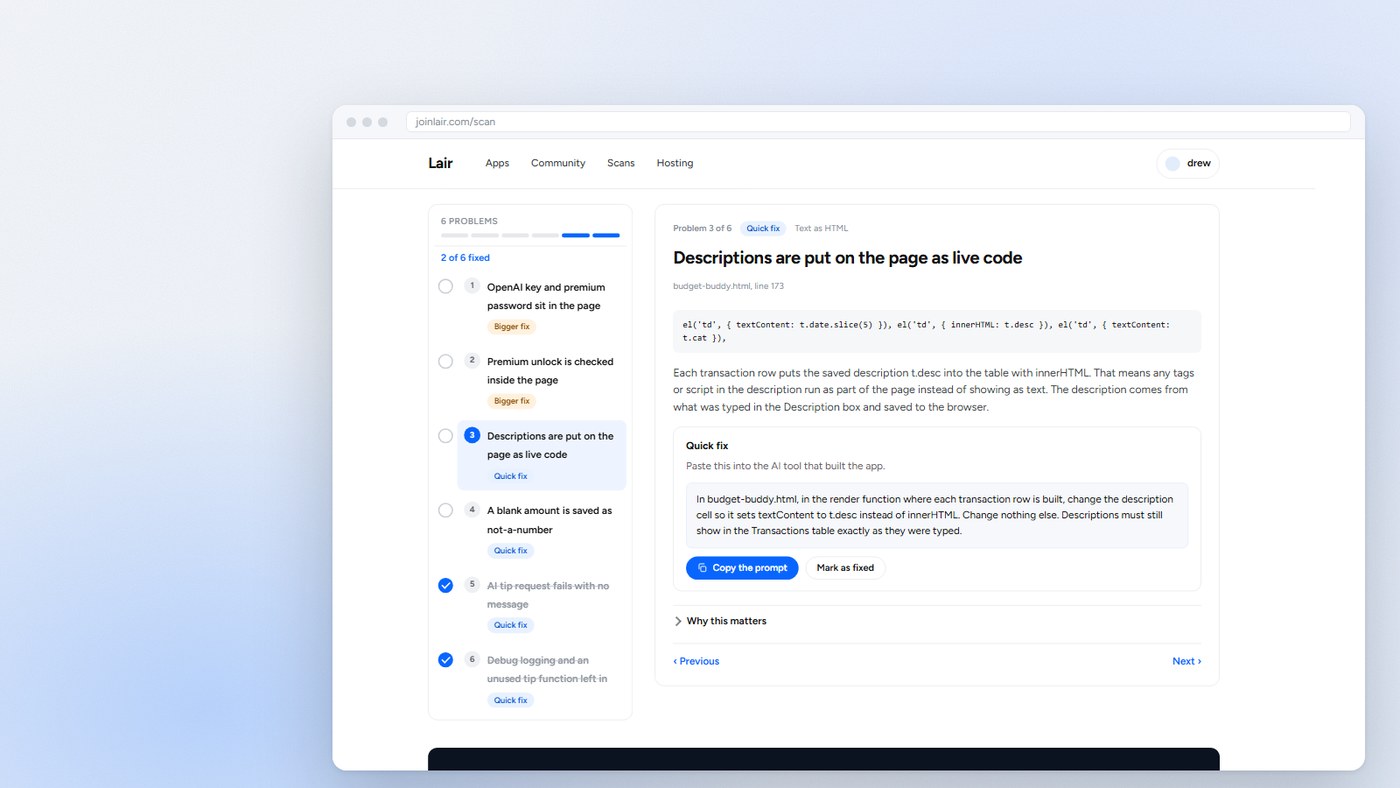
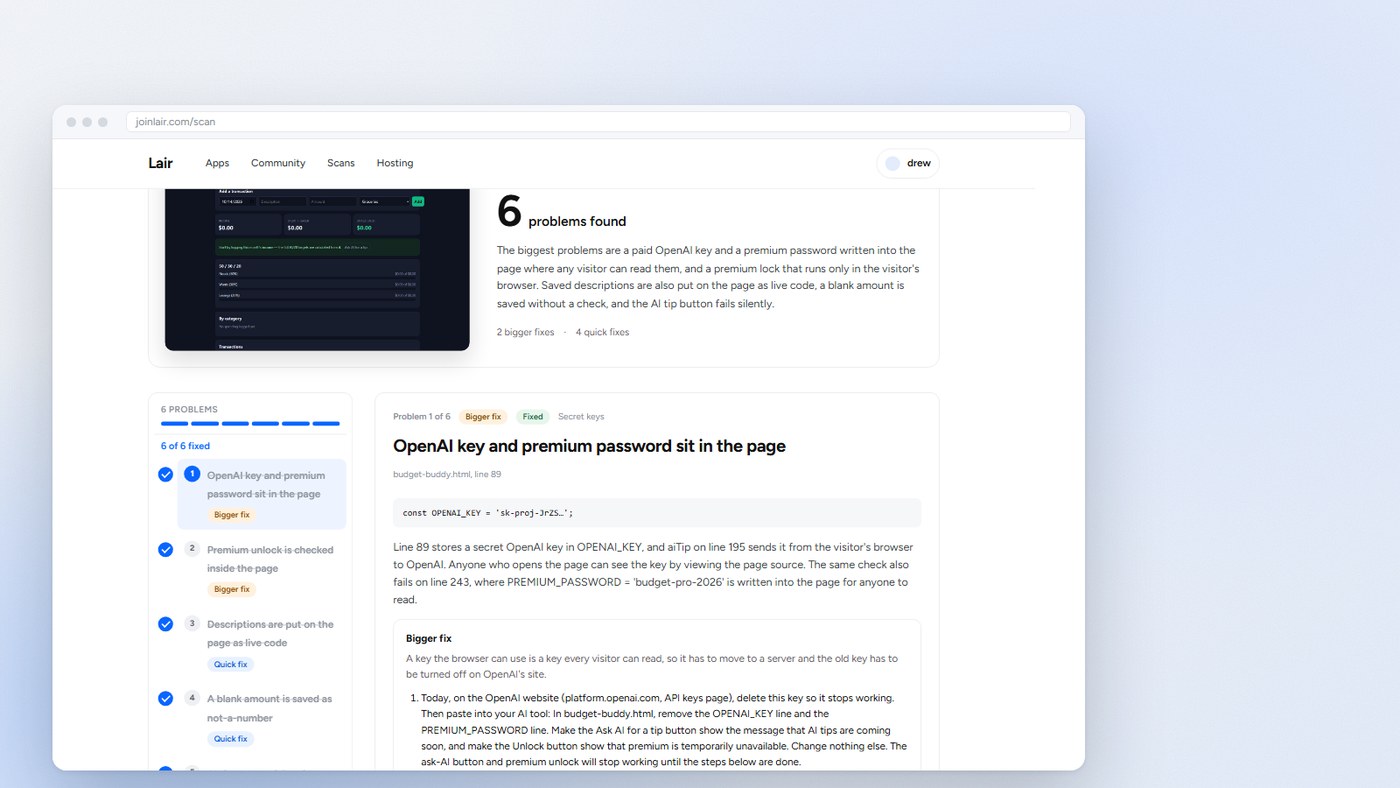
Secret keys sitting in the page where anyone can read them. Typed text put on the page as live code. Saved data trusted without a check. Requests that fail with no message, so the app looks fine while it is not.
For an app with a server: passwords stored in the open, file names that can reach outside their folder, redirects that can send a visitor anywhere.
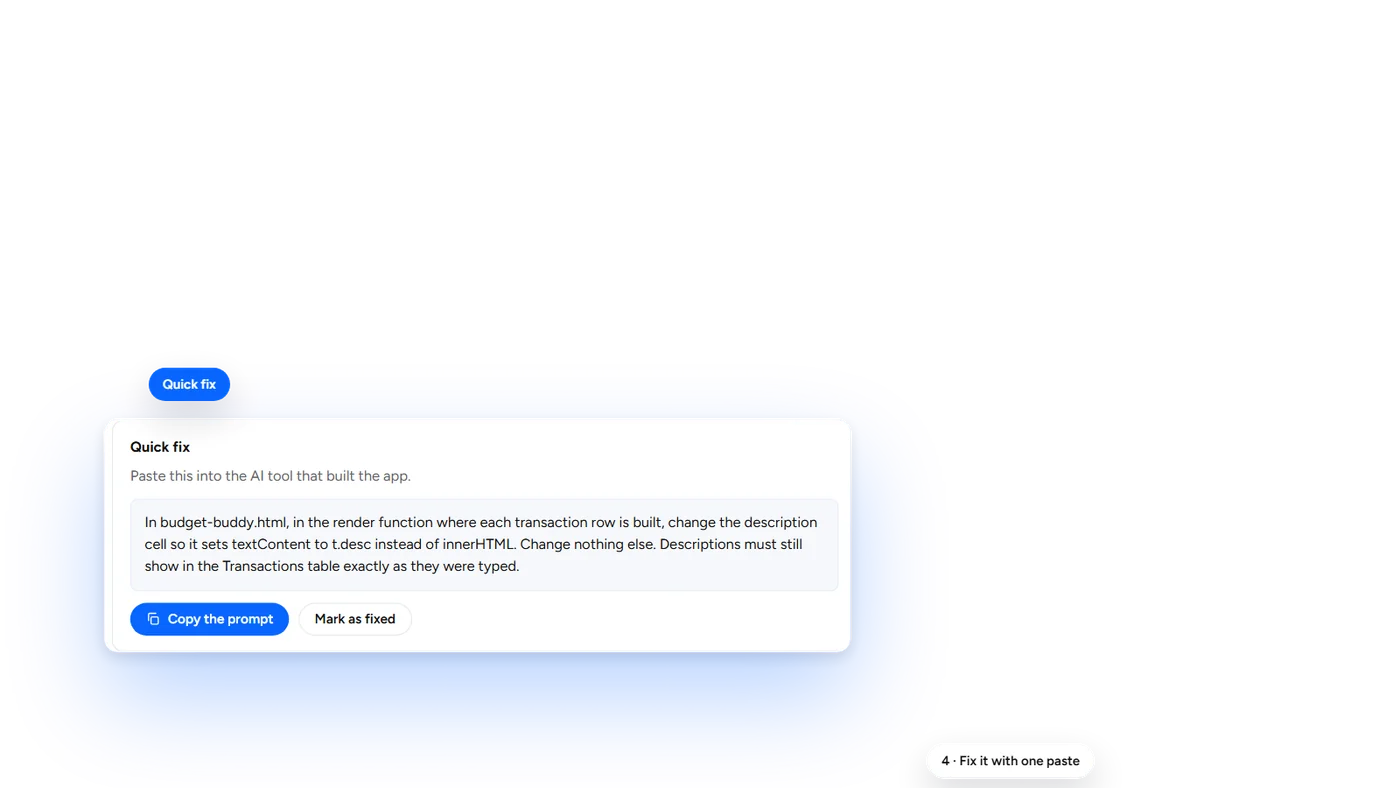
Each one comes back with the exact line, what goes wrong there in your app's own names, and a fix you can paste.